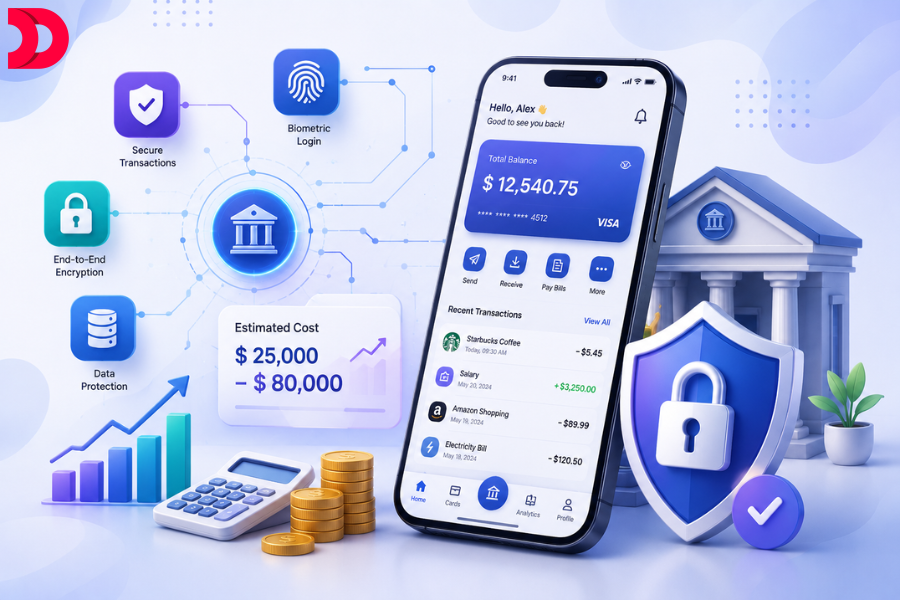
Nowadays, Mobile App security is very important. Every mobile app stores confidential data, including users’ personal details, payment information, login credentials, location data, customer records, and sensitive documents. One silly mistake and your mobile application will be exposed to cyberattacks, unauthorized access, and data breaches. A mobile app can be easily compromised through third-party APIs, the app’s code, backend services, libraries, and the device itself.
You may ask how to prevent cyber threats. Well, the answer is simple! By following these 4 mobile app security practices, such as authentication, encryption, secure data storage, and API security, businesses can easily protect their mobile apps from malware and reverse engineering while keeping the user’s data safe. Let’s discuss the 4 Mobile app security practices in detail.
Core components to follow for your Mobile App Security
Mobile app Authentication is the first step and ensures that genuine users have access to the mobile app. One of the most important practices companies should follow is preventing unauthorized access to the company’s personal details and confidential information. The following are the types of Authentication a business should implement on the website.
- Multi-Factor Authentication (MFA)
In Multi-factor authentication, users must bypass 2 or more security mechanisms to access the application. First, by entering the standard password, and second, by entering a code sent to you via text/email to ensure that the authenticated user is accessing the account.
Combining Multi-Factor Authentication with biometric integration can take your mobile application security to the next level. Instead of simply entering passwords, biometric authentication allows users to access the mobile app only if their fingerprints or face matches the stored record. So, even if a hacker somehow decodes your password, they won’t be able to match your fingerprints or face ID.
- Token-based Authentication
Each time a user logs in to the mobile app with a password, the authentication server provides 2 tokens: an access token (Short-lived JWT) and a refresh token. So, when a client tries to log in to your app, the app shares a unique access token with the client. Since it will be an access token, it can only last 10 to 15 minutes, preventing hackers from getting unauthorized access to the mobile app.
Implementing encryption in your mobile app helps you protect your personal and confidential information in 2 ways: at rest and in transit. Encryption is the process where readable data gets converted into unreadable data. It makes the information private and locked, requiring a special key, like a password, to decrypt the data.
Secure the user’s private information stored on a mobile device or server using a symmetric encryption algorithm such as AES-256. This method helps to store the data securely by converting it into an unreadable form. This way, even if a hacker gets access to the database, without the correct decryption key, they cannot access the user’s private information.
Millions of data travels across networks, and hackers constantly try to intercept it. To prevent this, encryption converts that data into an unreadable format while it travels so hackers cannot read it, but only the receivers can. To prevent this, HTTPS uses TLS to protect the internet connection between the mobile app and server by encrypting the information, making it hard for hackers to decrypt the data.
Mostly, Mobile apps store clients’ important information, such as login tokens & passwords, personal details, financial information, private messages, and locations, in the app itself so that the app can run fast and smoothly and even access it offline. However, if the brand does not store important information securely, it can be exposed to hackers, making it one of the major mobile app development challenges. How can it get exposed? Through insecure backups, through debugging, or through weaknesses in the app’s security.
Businesses should use the iOS Keychain and Android Keystore to securely manage sensitive information and encryption keys. Some of the keys even provide hardware-backed protection.
If your mobile app stores various clients’ structured data, then tools like SQLCipher can easily help to encrypt the database, so that a hacker cannot get access to the data without the proper key. Moreover, important information like passwords, APIs, or secret tokens shouldn’t be stored directly in SharedPreferences or UserDefaults.
Lastly, brands should store only the necessary sensitive information in their mobile app. If possible, do not store the user’s password or any other confidential information on the phone. This will reduce the risk of malware and interception.
An Application Programming Interface (API) is a way for a mobile app to exchange information with a backend server, and API security is crucial. Why? Hackers try to find security weaknesses by examining the communication between the app and the server. They usually try to modify request parameters and gain unauthorized access to the mobile app.
- Invalid Validation and Sanitization
Developers should verify each input arriving at the backend to ensure that it is not malicious. For example, in a login form, if someone tries to enter malicious code instead of a username, the system should validate and sanitize the input before it reaches the backend server, preventing your mobile app from being vulnerable to attacks like SQL injection.
- Control API request frequency
The team should set the limit to how many requests a user can send from the same IP address. If someone repeatedly tries to guess the password for login, it could be a hacker. Then the system should limit or temporarily block the user’s IP address, reducing the risk of brute-force login attacks and server overload.
- Architectural Offloading (API Gateway)
Implement an API Gateway layer that works as a security checkpoint. It checks the request before it reaches the main server. API Gateway helps verify tokens, apply security rules, and prevent suspicious traffic from entering the backend system.
Common Vulnerabilities to Look After in Mobile Applications
During the mobile app development process, developers should look out for these common vulnerabilities, as shown below
- Insecure data storage: If the brand is not storing users’ personal information or data securely, it can allow hackers to easily get unauthorized access to the user’s confidential data. For ex: storing passwords without encryption.
- Weak Authentication: If password security is weak and MFA (Multi-Factor Authentication) is not deployed in the app, it allows hackers to easily gain access to the mobile application.
- Improper Session Management: Brands should manage the app login session properly. If not, hackers may try to steal another user’s session token to gain unauthorized access to the app or their account.
- Broken Cryptography: If brands use weak encryption or cannot securely manage the encryption keys, then sensitive data could be easily exposed. For example, protecting users’ personal information with weak encryption.
- Injection Attacks: Developers must regularly check user input, as attackers can easily manipulate the app by entering harmful SQL code into the login page or system.
- Vulnerable third-party components: Teams must ensure they use updated and secure third-party libraries and software. Using outdated components or libraries with security vulnerabilities can allow attackers to easily gain unauthorized access to the mobile app or system.
Mobile app security best practices
Now that we have learned about the 4 core components brands must implement in their mobile app security, let’s also learn how brands can keep their mobile app security at the top by simply following these best practices as given below
- Regular code review and App testing
Secure mobile applications by simply following regular code reviews and app testing. Developers should make a habit of regularly reviewing code and testing to ensure the app is not vulnerable to security issues, so that if any user tries to exploit it, they can take immediate action to fix them early on.
Outdated software components, libraries, and frameworks make the application vulnerable to security risks. Make sure to regularly update your mobile application to minimize the risk of cyberattacks. Moreover, a regularly updated mobile app tells users that the app is secure and trustworthy to use.
- Ongoing Security Testing and Dependency Protection
Along with manual reviews, teams can also use Automated tools such as SAST and DAST to scan the app’s source code for malware, bugs, errors, and security issues before the code is forwarded for deployment. Teams can also use the Mobile Security Framework (MobSF), which is a security testing tool that helps to analyze the mobile application. Leverage dependency scanners like Snyk and Dependabot regularly to detect any security vulnerabilities in the app’s third-party libraries and software.
- Runtime Security and Environment Monitoring
Teams should check whether the mobile app is running on a rooted/jailbroken phone, emulator, or debugger. Using tools like Frida helps teams analyze the app’s behavior and detect whether anyone is trying to modify or manipulate it. If you detect any unusual activity in the app, then the team should restrict any sensitive features and send the alert message to the backend security system.
- Code Security and Architectural Protection
Make your app’s code difficult to read so attackers cannot easily copy code or understand it. For Android apps, teams can use tools like ProGuard and R8 to securely encrypt the app’s code. Do not store the app’s important data, passwords, tokens, and encryption keys in the repository code, as hackers can easily manipulate the code to gain access to the user’s data. Lastly, always check the information input by users. Teams should use Parameterized queries to prevent attacks like SQL injection.
Elevate your Mobile App Security with DevsTree
Mobile App security is not only about preventing cyberattacks and security risks but also keeping your software safe and successful in the long run. A secure Mobile application means earning customer loyalty, enhancing brand reputation, and protecting your users’ data. However, there are so many companies that offer mobile app security; it is important to choose the right one that fits your budget. This is where DevsTree, a trusted IT firm, comes into play. At DevsTree, we authenticate, encrypt, perform security testing, and offer post-launch maintenance to ensure your business is protected from security risks.
Investing in your Mobile app security is not a burden but a smart decision for protecting your app from attacks, and that is very important for long-term growth and staying ahead of your competitors. Check if your Mobile application has any vulnerabilities. Use tools like OWASP, AppScan, ProGuard, and Firebase App Check today. Still thinking? Hire Mobile app developers today and keep your business free from any security risks, and turn your app into something that users can trust because, honestly, keeping users’ data safe is the most important thing for a brand.
Conclusion: Build a secure Mobile App
Are you tired of your Mobile app consistently getting vulnerable to hackers? You’ve tried several tricks, apps, and tools to keep your mobile app safe, yet you are still here searching in the browser for “Mobile App Security”. We understand the frustration, but you have our back. Experiencing data breaches, threats, and cyberattacks can lead to loss of trust, financial losses, and damage to a company’s reputation. DevsTree makes app security very simple and effective. We not only identify vulnerabilities in your mobile app, but also help keep it safe, secure, and reliable for future growth. No more scrolling on the internet for the best Mobile app security company; you’ve found the best one.





 Sep 08, 2026